If you liked this webinar, you may also be interested in:
Incorrect or incomplete tiering makes it harder to identify which vendors pose the greatest exposure, spreading scarce resources too thin.
Why it Matters
Risk tiering is the mechanism that turns a large vendor inventory into a manageable set of priorities. It determines which vendors require deeper evidence, stronger contractual protections, and closer monitoring.
The organization’s tiering model may be correct, but a polished tiering model cannot compensate for unreliable or incomplete inputs. If vendors are placed into incorrect tiers (or not placed in a tier at all), every decision that follows can also be wrong. Lower risk relationships can absorb disproportionate attention while vendors tied to critical operations or sensitive data receive too little scrutiny.
"We probably have tens of thousands of vendors and all we've risk rated since I've been here has been like 4,000." -- TPRM Leader commenting on their risk tiering abilities
Risk tiers depend on accurate vendor data. Organizations may be making prioritization decisions from an unreliable foundation without receiving the necessary responses and evidence from their vendors.
What the Evidence Shows
- New 3rd party research coming soon from HITRUST and CHIME* surveyed over 100 qualified TPRM leaders and found that difficulty obtaining vendor information ranked as the second most important challenge in the CHIME survey, with risk confidence following close after.

- The KPMG 2026 Global Third-Party Risk Management survey identified that only 15% of TPRM leaders had high confidence in the data that underpins their program, and only 18% were fully integrated with Enterprise Risk Management (ERM).
What TPRM Leaders Can Do
- Define tiering criteria around the business impact of vendor failure, the sensitivity of data involved, system access, operational dependency, and downstream reliance.
- Align assurance requirements with each tier instead of applying the same questionnaire or review depth to every vendor.
- Revisit a vendor’s tier when its service scope, data access, dependencies, or operational role changes.
- Document and make visible exceptions and overrides so business pressure does not quietly weaken the tiering model.
- A defensible TPRM program directs the strongest evidence and most experienced judgment toward the relationships that can create the most consequential loss.
Coming Up in the Next Blog in the Series
If you missed the first blog in the series, please check out it here. Be sure to follow HITRUST on LinkedIn and X to know when the next blog in the TPRM Top 10 series, Limited Visibility into the Deep Supply Chain, is posted.
*CHIME Digital Health Analytics. Third-Party Risk Management Assurance: Strategic Market Validation Survey. Commissioned by HITRUST. Ann Arbor, MI: College of Healthcare Information Management Executives, Digital Health Analytics 2026. In July 2026, HITRUST commissioned CHIME Digital Health Analytics to conduct a blinded market-validation survey of 102 qualified respondents from separate healthcare provider organizations with more than $1 billion in annual revenue. Respondents represented security and GRC leadership, TPRM ownership, procurement and vendor management, legal and contracting, and executive leadership. Every participating organization actively managed at least 200 third-party vendors, and 87% managed more than 500.
The TPRM Top 10 - Incorrect or Incomplete Risk Tiering Is Directing Attention to the Wrong Places The TPRM Top 10 - Incorrect or Incomplete Risk Tiering Is Directing Attention to the Wrong Places
Artificial intelligence is transforming how organizations build, deploy, and secure technology. At the same time, it is creating new challenges for third-party risk management, assurance, and trust validation. To help organizations keep pace, HITRUST has introduced a series of innovations designed to make validated assurance more relevant, easier to use, more cost-effective, and more trustworthy in the AI era. These innovations include expanded AI and post-quantum coverage in HITRUST CSF v11.9, the new Report Center for trusted report sharing, and Questionnaire Responder, an AI-powered tool in MyCSF that helps organizations respond to security questionnaires faster and with greater confidence.
Among these innovations, Questionnaire Responder addresses one of the most persistent and resource-intensive challenges facing vendor, supplier, IT, security, and compliance teams today: the endless cycle of third-party security questionnaires.
The Challenge with Security Questionnaires
Organizations routinely receive questionnaires ranging from dozens to hundreds of questions. Each questionnaire can be different, which turns the process into repetitive work: locating evidence, validating information, drafting responses, and maintaining consistency across submissions. This burden grows as organizations support larger customer bases and more complex assurance demands.
For individuals responsible for responding to questionnaires, every hour spent answering repetitive questions is an hour not spent improving security posture, reducing risk, or supporting strategic initiatives. As assessment demands increase, the questionnaire process becomes more than an administrative burden; it becomes a constraint on the team’s ability to focus on higher-value work.
Introducing Questionnaire Responder
Questionnaire Responder is a new AI-powered tool within MyCSF that enables organizations to use data and evidence from their HITRUST assessments to automatically generate high-fidelity responses and related evidence requests. It evaluates questionnaires and uses the HITRUST assurance information in MyCSF to automatically answer cybersecurity, privacy, and AI security-related questions. Rather than relying on previous questionnaire responses or manually maintained knowledge bases, responses are grounded in validated HITRUST assessment information and supporting evidence.
How Questionnaire Responder Works
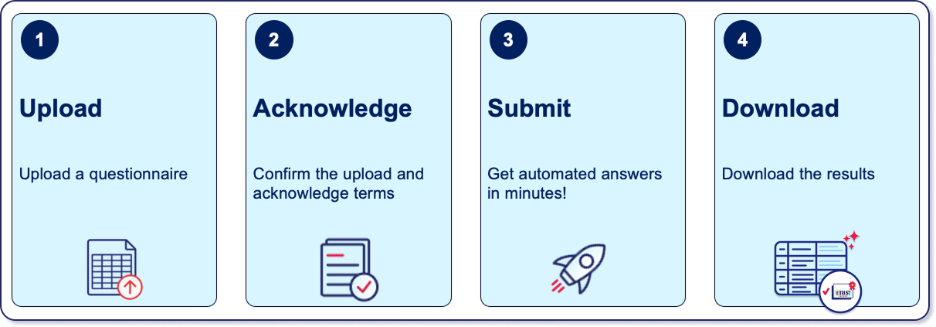
The process is straightforward and only takes a couple of clicks: a MyCSF user uploads a questionnaire, confirms the submission, submits it for processing, and minutes later can download the completed results in Excel format.

Built for Speed and Scale without Sacrificing Confidence or Quality
Current processes rely on document repositories, prior responses, internal wikis, or knowledge bases that can become outdated over time. Questionnaire Responder answers are generated from data and evidence backed by a HITRUST validated assurance to dramatically reduce response times. For example, with a HITRUST r2 assessment, Questionnaire Responder can complete up to 70% of related questions with 90% accuracy. For an 80-question questionnaire, organizations may save as much as seven hours between answering questions and gathering supporting evidence.
Growth often creates an unexpected challenge for security and compliance teams. As more customers, partners, and prospects request assurance information, questionnaire volume grows with them. Questionnaire Responder helps turn that growth from a manual workload problem into a scalable response process.
Early Access Begins Soon
Questionnaire Responder will be available through an Early Access program beginning October 26, 2026, with general availability planned for January 2027.
For organizations looking to reduce questionnaire fatigue, improve efficiency, and make better use of their HITRUST assurance investments, Questionnaire Responder offers a more scalable way to manage security questionnaire responses.
Interested in learning more? If you’re a HITRUST customer, contact your Customer Success Manager, or reach out to learn more and get a demo.
Innovation That Helps Trust Scale: Introducing Questionnaire Responder Innovation That Helps Trust Scale: Introducing Questionnaire Responder
Vague scopes, inconsistent assurance methods, and limited exception reporting can obscure material control gaps until a vendor has already been approved.
Why it Matters
Vendor due diligence is intended to identify material weaknesses before the organization commits to the relationship. In practice, TPRM teams often receive evidence that is difficult to interpret or incomplete for the product or service being provided. Reports may be unclear about what was tested, which systems were included, or how deeply controls were evaluated.
“You don’t understand fully what they actually tested versus what they didn’t." --TPRM Leader commenting on their assurance review process
HITRUST conversations with TPRM leaders identified that material risks can remain obscured even when documentation is available. TPRM leaders reported receiving assurance reports that were vague about scope, exceptions, and shared responsibilities. This forces TPRM analysts to interpret inconsistent evidence and request supplementary information before they can determine whether an identified weakness is relevant to the systems or services on which the organization depends.
This creates a dangerous form of uncertainty. Documentation may be available, but the team still cannot determine whether the evidence covers the product or services on which the organization will rely. Additional follow-up requests may close some gaps, but they also increase review time and vendor friction.
What the Evidence Shows
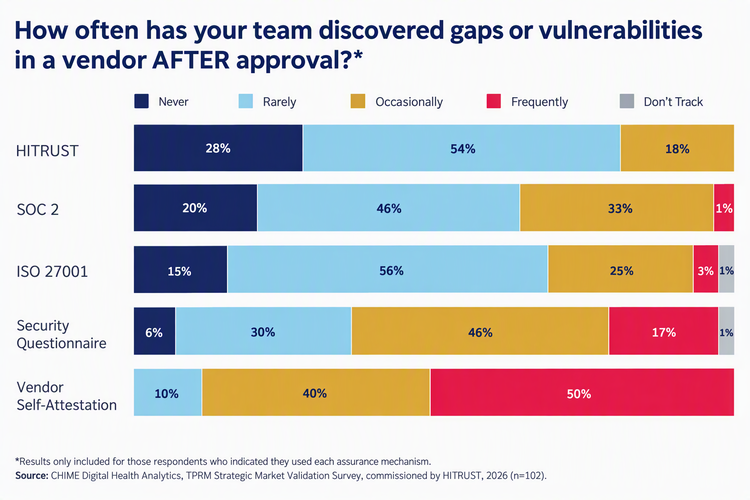
New 3rd party research coming soon from HITRUST and CHIME* surveyed over 100 qualified TPRM leaders and found that:
- 100% of organizations reported that their TPRM team discovered at least one gap or vulnerability in a vendor after approval, with 18.6% of the programs frequently identifying gaps or vulnerabilities.
- 16.7% of respondents reported that they frequently discovered vendor gaps after approval when only using security questionnaires.
- However, when organizations evaluated vendors using a third-party verified assurance mechanism (i.e. HITRUST, SOC 2, or ISO 27001) only 2.9% of programs frequently had a vendor gap or vulnerability after approval (and none were frequent when using HITRUST)
Additionally, the 2026 Panorays CISO Survey for Third-Party Cyber Risk Management found that “while 60% of CISOs report an increase in third-party security incidents, only 15% say they have full visibility into those risks.”
What TPRM Leaders Can Do
- Require evidence that clearly identifies scope, control coverage, exceptions, and shared responsibilities.
- Evaluate whether the assurance applies to the specific service, data, and operational dependency under review.
- Use independently validated assurance for higher-risk vendors and define when supplemental evidence is still required.
- Connect identified gaps to remediation, mitigating controls, contractual protection, or explicit risk acceptance before approval.
Coming Up in the Next Blog in the Series
If you missed the first blog in the series, please check out it here. Be sure to follow HITRUST on LinkedIn and X to know when the next blog in the TPRM Top 10 series, Incorrect or Incomplete Risk Tiering Is Directing Attention to the Wrong Places, is posted.
*CHIME Digital Health Analytics. Third-Party Risk Management Assurance: Strategic Market Validation Survey. Commissioned by HITRUST. Ann Arbor, MI: College of Healthcare Information Management Executives, Digital Health Analytics 2026. In July 2026, HITRUST commissioned CHIME Digital Health Analytics to conduct a blinded market-validation survey of 102 qualified respondents from separate healthcare provider organizations with more than $1 billion in annual revenue. Respondents represented security and GRC leadership, TPRM ownership, procurement and vendor management, legal and contracting, and executive leadership. Every participating organization actively managed at least 200 third-party vendors, and 87% managed more than 500.