If you liked this webinar, you may also be interested in:
Trusting AI Requires More Than Trusting the Vendor
Satya Nadella recently posted about how to run powerful AI inside the enterprise, and one line in it should change how risk teams think. Validation, he wrote, must be independent of the thing being validated. He also said a model provider’s assurances don’t relieve the customer of responsibility. His post is about enterprises containing their own AI, but the principle applies to anyone relying on a third party.
AI is creating a challenge the assurance industry has never had to solve at scale. Traditional software typically behaves within predefined boundaries. Modern AI systems can reason, invoke tools, access enterprise data, and act on behalf of users.
The AI supply chain is rapidly becoming more complex than the software supply chain. As organizations increasingly rely on third-party AI, they are accepting risk from systems they did not build, cannot inspect, and often cannot independently test. That changes the question from "Does this vendor have AI?" to "What evidence exists that this AI operates within verified security boundaries?" The future of AI trust will be determined by how that question gets answered.
If a vendor is the only source of evidence about its own AI controls, you don’t have assurance. You have a claim. The vendor built the system, wrote the policies, and is now describing how well both work. Nadella’s point is that this arrangement shouldn’t be accepted, and he calls for industry standards where existing ones fall short.
What Programs Are Getting Today
In practice it comes down to two things.
The first is a questionnaire. A few AI questions get added to the existing set, the vendor answers them, and the answers go in the file. Nobody can say whether those were the right questions, whether the answers are accurate, or whether two vendors who both said “yes” meant the same thing. This is self-reporting, and no one independent has looked.
The second is a governance assurance, such as ISO 42001. That’s a real step up, and it’s independent. It tells you the vendor has a management system for AI: policies, roles, risk processes, accountability.
But governance and security are different questions. A management system standard tells you the vendor has a process for managing AI risk. It doesn’t tell you whether the model’s access to your data is limited to what it needs, whether prompt injection has been tested, whether actions are logged in a way that survives an investigation, or whether anyone can shut an agent down mid-task. A vendor can have mature AI governance and still have an agent with far too much access.
Where the Risk Actually Lives
Nadella’s post puts the weight on technical controls: separating the model from the harness that orchestrates it, limiting the action space, keeping safeguards outside the model, logging every meaningful action, and being able to contain a model from the start. The relevant questions are security questions:
- What can the AI reach, and who approved it?
- What can it do without a human signing off?
- Are those limits enforced outside the model, or does the system depend on the model behaving?
- Is there a tamper-resistant record of its actions?
- Can an authorized person stop it, and how fast?
- Has anyone tested it against attack, including misuse of connected tools?
- Which model providers and tools sit underneath, and what happens if one is compromised?
- When something fails, what does the customer get told, and when?
Questionnaires can ask about these but can’t verify them. Governance assurances generally don’t test them.
What TPRM Programs Need
Independent assurance over AI security controls, with a few properties:
- Independent. The party testing the controls didn’t build them and has no stake in the result.
- Explicit scope. You can see which AI systems were examined and which weren’t.
- Operating effectiveness. Controls were tested in practice, not just documented.
- Current. Models, prompts, and tool permissions change fast, so stale evidence misleads.
- Comparable. A common set of criteria lets you evaluate many vendors without a custom review for each.
Governance assurance and security assurance answer different questions, and a mature program should want both. The mistake is treating the first as a substitute for the second.
What to do This Quarter
Pull your last few AI-related vendor assessments and sort the evidence into three piles: self-reported answers, governance assurance, and independently tested security controls. Most programs will find the third pile nearly empty. That’s your gap.
Then change what you ask for. Skip the longer questionnaire. Ask which AI systems are in scope, who tested the security controls, against what criteria, and how recently.
The Caveat
Security assurance doesn’t prove a model’s outputs are correct or that it’s aligned with anyone’s intent. It tells you the vendor has limited what the AI can reach and do, can see what it’s doing, and can contain a failure. That shrinks the blast radius without eliminating the risk, and a good program should say so plainly.
But it’s the part buyers can demand today, and the part most programs are missing.
Trusting AI Requires More Than Trusting the Vendor Trusting AI Requires More Than Trusting the Vendor
Information Risk Has a Measurement Problem
Enterprises have invested heavily in cybersecurity, GRC programs, security ratings, and third-party risk management. Yet despite those investments, a fundamental business question remains unanswered: how much information risk does the organization truly face, and what could that exposure mean financially?
That gap represents one of the next major challenges for the information risk market: moving from collecting evidence about risk to consistently measuring the risk itself.
As organizations collect increasing volumes of security, compliance, and assurance evidence, the challenge is no longer obtaining information. It's determining what it means for information risk and residual risk. These inputs are difficult to interpret consistently and even harder to translate into comparable measures of residual information risk.
Financial markets rely on standardized measures to compare credit risk, evaluate exposure, and support consequential financial decisions. For example, the FICO score has been around for decades. Information risk has lacked an equivalent measurement system
The Measurement Gap Limits Informed Third-Party Risk Decisions
Without a common basis for comparison, security leaders, finance teams, executives, and boards still struggle to answer a shared set of questions about third-party risk:
- How much information risk remains?
- Which relationships create the greatest exposure?
- Are we operating within our risk appetite?
- Where will mitigation have the greatest impact?
- Which risks should we reduce, retain, or transfer?
- What might those exposures mean financially?
The absence of a common, explainable way to translate diverse security evidence into meaningful measures of third-party residual information risk and potential financial exposure creates a fundamental gap in how organizations understand and govern information risk. Without that foundation, governance and consequential decisions depend too often on fragmented evidence, inconsistent methodologies, and subjective interpretation.
Introducing IRIDX: From Evidence to Risk Measurement
IRIDX introduces a consistent, explainable approach to measuring residual information risk and estimating related financial exposure using the assurance evidence organizations already has to improve third-party risk management and governance.
IRIDX is not another assessment, certification, or questionnaire. It addresses the problem too many disparate and diverse artifacts creates: measurement.
IRIDX establishes a common measurement foundation for comparing risk, prioritizing action, and informing financial decisions. By evaluating existing assurance and risk evidence for relevance, rigor, and reliability, IRIDX produces standardized and explainable measures of residual information risk and related financial exposure.
The opportunity is to make information risk more measurable and comparable across the enterprise, creating a common foundation that security, risk, finance, executive leadership, and boards can use to make decisions.
IRIDX helps organizations make more informed and consequential decisions across three critical areas:
- Operational: Prioritize mitigation efforts, identify the highest-risk relationships, and improve the efficiency and scalability of risk reviews.
- Financial: Evaluate potential financial exposure and make more informed decisions about which risks to reduce, retain, or transfer.
- Governance: Compare exposure against risk appetite, identify material exceptions, and provide executives and boards with a consistent basis for oversight and accountability.
IRIDX and HITRUST: Distinct and Complementary Roles
IRIDX is a separate company under common ownership with HITRUST. HITRUST provides frameworks and independently validated cybersecurity assurance; IRIDX focuses on information risk ratings, residual-risk measurement, and financial exposure modeling.
IRIDX builds on nearly two decades of experience in cyber threat analysis, control development, and assurance methodologies. It develops and governs its methodologies under its own governance framework, separate from HITRUST's assurance and certification programs.
The Evolution of TPRM Begins Today
For too long, organizations have had more security evidence than they could consistently translate into business-relevant measures of risk. The next evolution of third-party risk management is not simply collecting more evidence. It is getting more value from the evidence organizations already have. By connecting assurance evidence to residual-risk measurement, financial exposure modeling, and governance, IRIDX opens new possibilities for how organizations understand, compare, reduce, retain, and transfer information risk.
The implications extend beyond TPRM. A consistent approach to measuring information risk creates the potential for a shared language across cybersecurity, enterprise risk, finance, executive leadership, boards, and ultimately other participants that need to understand information risk in business terms.
This is the beginning of a larger ambition: a common language for information risk that can support better cybersecurity, stronger governance, and more informed risk decisions.
To learn more, read the press release and visit IRIDX.com.
You Can't Govern What You Can't Measure. Introducing IRIDX You Can't Govern What You Can't Measure. Introducing IRIDX
Without timely reassessment, material changes in a vendor’s security posture can go undetected between formal reviews.
Why It Matters
Most assurance mechanisms provide a point-in-time view even when vendor environments continue to change after approval. Services expand, systems change, new downstream providers are introduced, and security incidents alter the risk profile. A review that was reasonable at onboarding might lose relevance before the next scheduled assessment.
“Modern businesses rely heavily on third-party partnerships to create value and drive innovation, but they are expanding faster than organizations can manage the risks. According to KPMG research, 83 percent of executives plan to expand their partner networks in the next one to three years, yet 71 percent admit that they have trouble getting their partners to align on goals.” - KPMG 2026 Global Third-Party Risk Management Survey
Limited monitoring also weakens the organization’s response to risk already accepted. A vendor approved with conditions may require enhanced oversight, time-bound remediation, or reassessment when a material event occurs. Without reliable triggers, the exception remains open while the business continues to depend on the service.
What the Evidence Shows
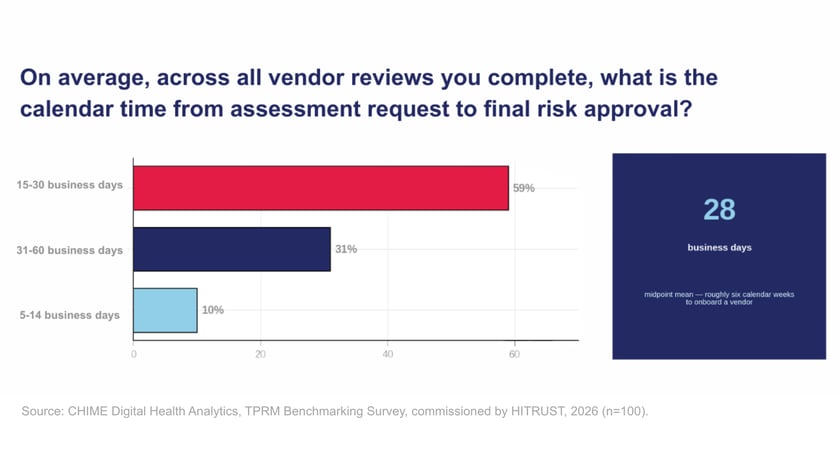
- New 3rd party research coming soon from HITRUST and CHIME* surveyed over 100 qualified TPRM leaders and found that the vendor approval process took a median of 28 days with almost 1/3 taking 31-60 days to complete.

- The Mitratech 2025 Third-Party Risk Management Study reported that only 29% of organizations could assess risk across the full vendor lifecycle, and that organizations actively monitored only 40% of their vendors on average.
What TPRM Leaders Can Do
- Set monitoring depth and reassessment frequency according to vendor risk and operational criticality.
- Trigger reassessment when service scope, system access, data handling, control ownership, or downstream dependencies materially change.
- Connect incident intelligence, remediation status, and monitoring data to the original approval decision.
- Apply enhanced monitoring and clear escalation paths to vendors operating under approved exceptions.
Continuous oversight does not require the same intensity for every vendor. It requires enough risk-based monitoring to recognize when the facts behind an earlier decision have changed.
Coming Up in the Next Blog in the Series
If you missed the first blog in the series, please check out it here. Be sure to follow HITRUST on LinkedIn and X to know when the last blog in the TPRM Top 10 series, Closing Perspective on The TPRM Top 10, is posted.
*CHIME Digital Health Analytics. Third-Party Risk Management Assurance: Strategic Market Validation Survey. Commissioned by HITRUST. College of Healthcare Information Management Executives, Digital Health Analytics 2026. Survey of 100 third-party risk management practitioners at U.S. healthcare provider organizations with annual revenue of $1 billion or more, fielded August 2026.