If you liked this webinar, you may also be interested in:
Vendor populations are expanding faster than TPRM teams can add staffing and review capacity, leaving parts of the vendor portfolio under-reviewed.
Why It Matters
Third-party ecosystems now include cloud providers, software companies, data processors, managed service providers, consultants, and other external parties. Each relationship can extend cybersecurity, privacy, compliance, and resilience risk beyond the organization’s direct control. Yet the teams responsible for reviewing those relationships remain comparatively small.
The result is a capacity problem with direct business consequences. When assessment demand exceeds available resources, TPRM programs must choose which vendors receive a thorough review, which receive limited scrutiny, and which wait in a growing queue. Procurement slows, onboarding becomes a bottleneck, and full-portfolio due diligence becomes increasingly difficult to sustain.
“You're not able to actually do due diligence on your full vendor portfolio because you don't have enough people." -- TPRM Leader commenting on their capacity concerns
What the Evidence Shows
New 3rd party research coming soon from HITRUST and CHIME* surveyed over 100 qualified TPRM leaders and found that:
-
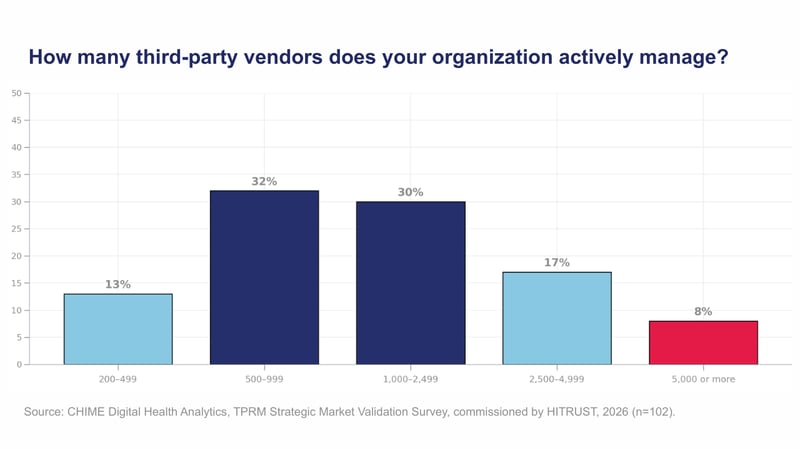
Nearly 55% of surveyed organizations manage more than 1,000 vendors, and almost 25% manage more than 2,500.

-
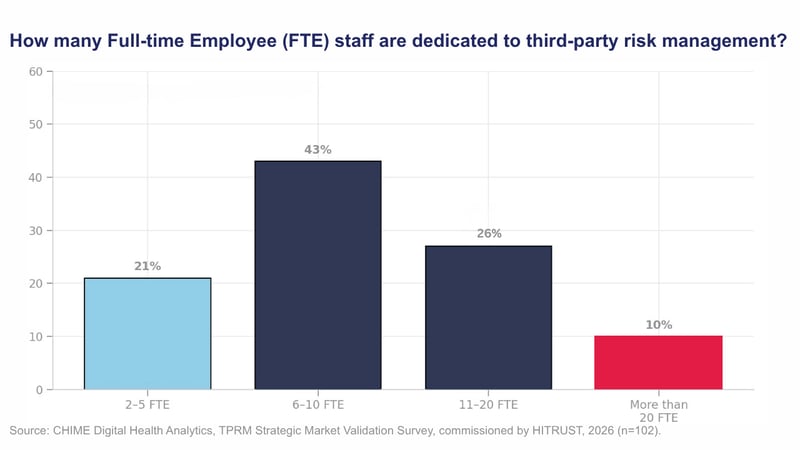
Only 9.8% reported more than 20 dedicated TPRM personnel.

-
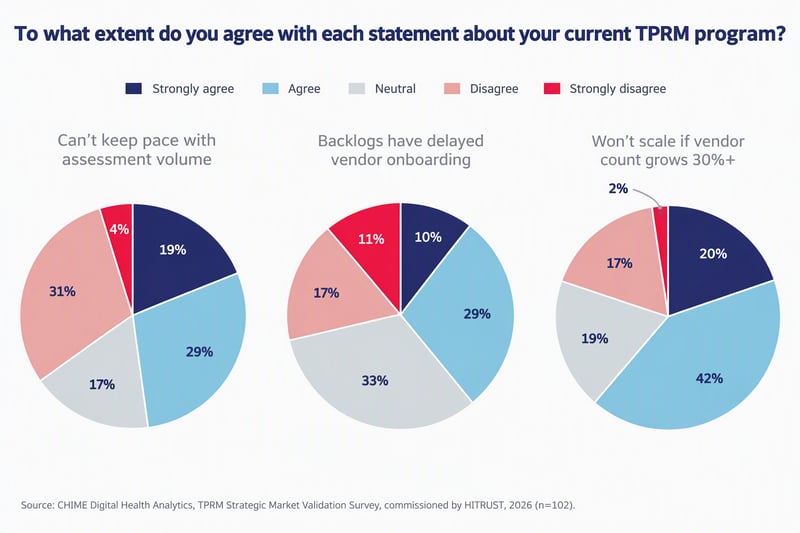
Almost 62% agreed that their programs would not scale if vendor counts increased by more than 30%.
- 48% of TPRM leaders agreed they can’t keep pace with assessment volume, while 39% indicated they already have backlogs which have delayed vendor onboarding.

External research also reinforces these findings:
- The Venminder State of Third-Party Risk Management 2025 paper reports, “Despite managing more vendors, TPRM staffing has not increased proportionally. Programs with 1-2 full-time employees rose from 43% to 48%, while those with 6-10 FTEs dropped significantly (from 10% to 4%).”
- The Ncontracts State of Third-Party Risk Management 2026 report states, “Most TPRM programs operate with minimal staffing while managing substantial vendor portfolios. Nearly two-thirds (63%) run on just 1-2 dedicated employees, and another 13% have no dedicated staff at all. At the same time, over half (53%) manage 300+ vendors, creating ratios where individual professionals oversee 100+ vendor relationships.”
What TPRM Leaders Can Do
- Apply risk-tiered assurance so the most rigorous reviews are reserved for the relationships capable of causing the greatest harm.
- Use standardized, independently validated assurance to reduce repetitive review work and reliance on one-off evidence requests.
- Automate evidence collection, control mapping, reminders, and routine reassessment activity where human judgment is not required.
While all vendors should be known and risk-tiered, the goal is not to review every vendor in exactly the same way. It is to preserve meaningful coverage as the vendor population grows, without allowing speed to replace rigor or backlogs to define the risk strategy.
Coming Up in the Next Blog in the Series
If you missed the first blog in the series, please check out it here. Be sure to follow HITRUST on Linkedin and X to know when the next blog in the TPRM Top 10 series, Critical Vendors Become Too Important to Fail, is posted.
*CHIME Digital Health Analytics. Third-Party Risk Management Assurance: Strategic Market Validation Survey. Commissioned by HITRUST. Ann Arbor, MI: College of Healthcare Information Management Executives, Digital Health Analytics 2026. In July 2026, HITRUST commissioned CHIME Digital Health Analytics to conduct a blinded market-validation survey of 102 qualified respondents from separate healthcare provider organizations with more than $1 billion in annual revenue. Respondents represented security and GRC leadership, TPRM ownership, procurement and vendor management, legal and contracting, and executive leadership. Every participating organization actively managed at least 200 third-party vendors, and 87% managed more than 500.
The TPRM Top 10 - Vendor Growth Is Outrunning TPRM Capacity The TPRM Top 10 - Vendor Growth Is Outrunning TPRM Capacity
Third-party Risk Management (TPRM) was built to help organizations understand and govern risk beyond their walls, but the operating model is being overtaken by the ecosystem it is meant to control. Vendor populations are expanding, critical dependencies are deepening, and the evidence used to make decisions is often incomplete, inconsistent, or already out of date.
The uncomfortable truth is that many programs are still organized to process assessments while the business needs them to manage an ecosystem and the associated risks. The result is a widening gap between the volume and speed of third-party risk and the capacity of TPRM programs to respond. Teams spend scarce expertise chasing documents, interpreting incomparable reports, and revisiting basic facts instead of identifying the exposures most capable of disrupting critical operations or compromising sensitive data.
Why This Is Needed Now
Third-party dependence has crossed from a procurement concern into a material source of enterprise exposure. Organizations are adding vendors, concentrating critical operations in a smaller number of providers, inheriting deeper supply-chain dependencies, and relying on point-in-time reviews while risk changes continuously.
The evidence shows that the operating environment is accelerating faster than the traditional review cycle:
- Nearly half of breaches now reach the enterprise through the ecosystem: the 2026 Verizon Data Breach Investigations Report found that 48% of breaches involved a third party, a 60% year-over-year increase.
- The World Economic Forum reported that 54% of large organizations identify supply-chain interdependencies as the greatest barrier to achieving cyber resilience.
- KPMG found that only 15% of TPRM leaders have high confidence in the data underpinning their programs, while just 18% report that TPRM is fully integrated with enterprise risk management.
New research coming soon from HITRUST and CHIME* surveyed over 100 qualified TPRM leaders and found that:
- Nearly 55% of surveyed organizations manage more than 1,000 vendors, yet only 9.8% reported more than 20 dedicated TPRM personnel.
- 62% said their programs would not scale if vendor counts increased by more than 30%
- 48% said they cannot keep pace with assessment volume
- 39% reported onboarding delays caused by backlogs
- Every surveyed organization reported discovering at least one vendor gap or vulnerability after approval
- 23% said a vendor incident had caused clinical or operational disruption
The constraints are not on how much organizations spend. Although 81.4% of respondents reported annual TPRM program costs of at least $1 million, cost ranked last among the challenges presented. TPRM leaders placed greater emphasis that their operating model produces timely, trustworthy decisions at scale.
Together, the issues describe an interconnected operating problem: How can TPRM programs scale without sacrificing the rigor, timeliness, and confidence required to protect critical operations and data?
Introducing the TPRM Top 10
The operating problem facing TPRM leaders is no longer whether third-party risk matters. It is where to focus limited resources, expertise, and investment when vendor ecosystems are expanding faster than traditional review models can keep up. Answering that question requires moving beyond general concern and identifying the operational challenges most likely to determine whether TPRM can scale with the business, sustain confidence in risk decisions, and protect critical operations and data.
The TPRM Top 10 is a new perspective on the most pressing issues confronting modern third-party risk programs. These issues are the ones shaping board discussions, slowing vendor decisions, and consuming scarce expertise. Developed from HITRUST’s ongoing work with TPRM leaders and practitioners responsible for complex third-party ecosystems, it reflects what programs are seeing in the field and where they believe change is most urgently needed.
This list is not presented as a universal ranking or approach for all organizations. Instead, it is intended as a practical guidance for TPRM leaders to modernize their programs. Together, these issues define the work required to move from process-centered vendor review to a more scalable, evidence-driven, and enterprise-relevant model for managing third-party risk.
|
# |
Issue |
What it means |
|
1 |
Vendor Growth Is Outrunning TPRM Capacity |
Vendor populations are expanding faster than TPRM teams can add staffing and review capacity, leaving parts of the vendor portfolio under-reviewed. |
|
2 |
Critical Vendors Become Too Important to Fail |
Some vendors are so critical to business functions that organizations have little practical ability to reject or replace them, even when assessments identify material concerns. |
|
3 |
Lack of Assurance Comparability |
Inconsistent scoring and reporting methods make it difficult to compare assurance reports and results across vendors. |
|
4 |
Manual Work is Consuming TPRM Capacity |
Spreadsheets, questionnaires, and disconnected tools consume capacity that should be spent evaluating and reducing risk. |
|
5 |
Hidden Vendor Risks |
Vague scopes, inconsistent assurance methods, and limited exception reporting can obscure material control gaps until a vendor has already been approved. |
|
6 |
Incorrect or Incomplete Risk Tiering Is Directing Attention to the Wrong Places |
Incorrect or incomplete tiering makes it harder to identify which vendors pose the greatest exposure, spreading scarce resources too thin. |
|
7 |
Limited Visibility Into the Deep Supply Chain |
Organizations often lack a clear view of the subcontractors and other downstream parties supporting their most critical vendors. |
|
8 |
Concentration Risk Turns Vendor Failures Into Enterprise Events |
Heavy dependence on a small number of providers can turn one vendor incident into a broader enterprise disruption. |
|
9 |
Unreliable Vendor Data Undermines Risk Decisions |
Incomplete or unreliable information weakens risk decisions and delays action. |
|
10 |
Vendor Risk Changing Faster Than Reassessment Cycles |
Without timely reassessment, material changes in a vendor’s security posture can go undetected between formal reviews |
Addressing the Top 10 in Practice
This blog launches a series of posts that will explore each of the ten issues in greater detail including why it matters, what the evidence shows, and what TPRM leaders can do to respond. Be sure to follow HITRUST on LinkedIn and X to know when the next blog in the series is posted.
* CHIME Digital Health Analytics. Third-Party Risk Management Assurance: Strategic Market Validation Survey. Commissioned by HITRUST. Ann Arbor, MI: College of Healthcare Information Management Executives, Digital Health Analytics 2026. In July 2026, HITRUST commissioned CHIME Digital Health Analytics to conduct a blinded market-validation survey of 102 qualified respondents from separate healthcare provider organizations with more than $1 billion in annual revenue. Respondents represented security and GRC leadership, TPRM ownership, procurement and vendor management, legal and contracting, and executive leadership. Every participating organization actively managed at least 200 third-party vendors, and 87% managed more than 500.
Traditional Third-Party Risk Management Has Reached Its Operating Limit Traditional Third-Party Risk Management Has Reached Its Operating Limit
Welcome to October, and to Cybersecurity Awareness Month. At HITRUST, we’re using the month to spotlight modern third-party risk management with new research, insights and expert perspectives, and preview product updates designed to help organizations work more efficiently and confidently. Here’s a look at what’s ahead.
Moving From Traditional to Modern TPRM
We’re going to be focusing on third-party risk management (TPRM) over the course of the entire month. Traditional TPRM programs are failing to keep up with the growth and complexity of an organization's vendor and supply chain ecosystem. Vendor populations are expanding, critical dependencies are deepening, and the assurance evidence used to make decisions is often incomplete, inconsistent, or already out of date. We know there is a better way, but the first step in the journey to a modern TPRM program is to recognize the issues on the path and know how to react.
More Product Innovation Ahead
Following the recent releases of Report Center and CSF v11.9.0, we’re announcing an exciting new AI-powered capability in MyCSF designed to help HITRUST certified organizations address a persistent, time-consuming challenge. We can’t share all the details yet, but we can say this: copying and pasting will soon be a thing of the past.
Hear From the Experts
October will offer several opportunities to hear practical perspectives from industry practitioners and security leaders addressing assurance, cyber risk, and vendor oversight challenges.
The second installment of our Assurance Gap webinar series, SOC 2 vs. HITRUST: A Practitioner Debate on What Third-Party Risk Actually Needs, takes place on October 8. Join TPRM and GRC experts Nick Norton, Ryan Patrick, and AJ Yawn as they discuss the strengths, limitations, and real-world applications of today's most common assurance approaches.
Looking for broader industry perspectives? HITRUST experts will also be participating in several industry events where the conversation will extend beyond compliance checklists to the future of cyber resilience and vendor risk. At the CHIME State of Cybersecurity event, we’ll join a panel of industry leaders to discuss the top priorities for CISOs over the next 90 days and how organizations are navigating an increasingly complex threat landscape.
Later in the month, our team will be speaking and exhibiting at Vendor & Third Party Risk USA, in Ft. Worth, TX. If you’re going, be sure to block time to head to Ryan Patrick’s breakout session, Rethinking Vendor Due Diligence: When Cyber Threats Outpace Traditional Assurance.
HITRUST will cap off a busy few weeks with a keynote at GRF Summit on Security & Third-Party Risk, where attendees will gain insights into emerging risks, evolving assurance expectations, and practical approaches for building greater trust across the vendor ecosystem.
If you're responsible for risk management, compliance, or vendor oversight, these sessions offer a chance to hear how peers and industry experts are addressing the challenges shaping the future of assurance.
Don’t Miss Out
If you don’t want to miss out on our content, product news, and events, subscribe to be notified and be sure to follow HITRUST on Linkedin and X. In the meantime, check out our recent Navigating AI Security and Assurance paper and our recent blogs.