If you liked this webinar, you may also be interested in:
Vague scopes, inconsistent assurance methods, and limited exception reporting can obscure material control gaps until a vendor has already been approved.
Why it Matters
Vendor due diligence is intended to identify material weaknesses before the organization commits to the relationship. In practice, TPRM teams often receive evidence that is difficult to interpret or incomplete for the product or service being provided. Reports may be unclear about what was tested, which systems were included, or how deeply controls were evaluated.
“You don’t understand fully what they actually tested versus what they didn’t." --TPRM Leader commenting on their assurance review process
HITRUST conversations with TPRM leaders identified that material risks can remain obscured even when documentation is available. TPRM leaders reported receiving assurance reports that were vague about scope, exceptions, and shared responsibilities. This forces TPRM analysts to interpret inconsistent evidence and request supplementary information before they can determine whether an identified weakness is relevant to the systems or services on which the organization depends.
This creates a dangerous form of uncertainty. Documentation may be available, but the team still cannot determine whether the evidence covers the product or services on which the organization will rely. Additional follow-up requests may close some gaps, but they also increase review time and vendor friction.
What the Evidence Shows
New 3rd party research coming soon from HITRUST and CHIME* surveyed over 100 qualified TPRM leaders and found that:
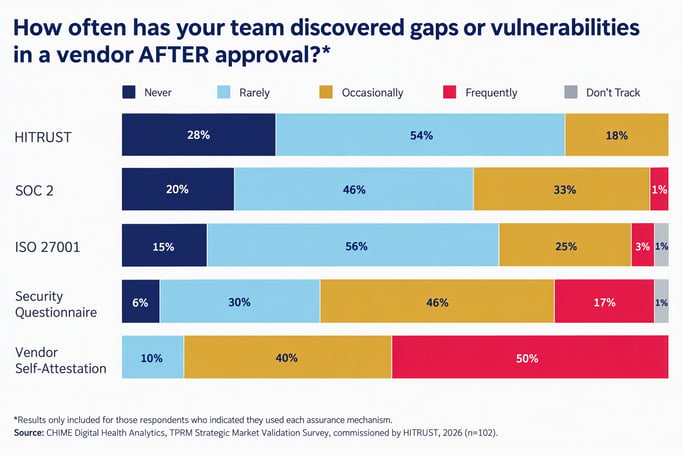
- 100% of organizations reported that their TPRM team discovered at least one gap or vulnerability in a vendor after approval, with 18.6% of the programs frequently identifying gaps or vulnerabilities.
- 16.7% of respondents reported that they frequently discovered vendor gaps after approval when only using security questionnaires.
- However, when organizations evaluated vendors using a third-party verified assurance mechanism (i.e. HITRUST, SOC 2, or ISO 27001) only 2.9% of programs frequently had a vendor gap or vulnerability after approval (and none were frequent when using HITRUST)
Additionally, the 2026 Panorays CISO Survey for Third-Party Cyber Risk Management found that “while 60% of CISOs report an increase in third-party security incidents, only 15% say they have full visibility into those risks.”
What TPRM Leaders Can Do
- Require evidence that clearly identifies scope, control coverage, exceptions, and shared responsibilities.
- Evaluate whether the assurance applies to the specific service, data, and operational dependency under review.
- Use independently validated assurance for higher-risk vendors and define when supplemental evidence is still required.
- Connect identified gaps to remediation, mitigating controls, contractual protection, or explicit risk acceptance before approval.
Coming Up in the Next Blog in the Series
If you missed the first blog in the series, please check out it here. Be sure to follow HITRUST on LinkedIn and X to know when the next blog in the TPRM Top 10 series, Incorrect or Incomplete Risk Tiering Is Directing Attention to the Wrong Places, is posted.
*CHIME Digital Health Analytics. Third-Party Risk Management Assurance: Strategic Market Validation Survey. Commissioned by HITRUST. Ann Arbor, MI: College of Healthcare Information Management Executives, Digital Health Analytics 2026. In July 2026, HITRUST commissioned CHIME Digital Health Analytics to conduct a blinded market-validation survey of 102 qualified respondents from separate healthcare provider organizations with more than $1 billion in annual revenue. Respondents represented security and GRC leadership, TPRM ownership, procurement and vendor management, legal and contracting, and executive leadership. Every participating organization actively managed at least 200 third-party vendors, and 87% managed more than 500.
The TPRM Top 10 - Hidden Vendor Risks The TPRM Top 10 - Hidden Vendor Risks
Spreadsheets, questionnaires, and disconnected tools consume capacity that should be spent evaluating and reducing risk.
Why It Matters
Many TPRM programs still depend on fragmented workflows. Teams track vendors in spreadsheets, distribute proprietary questionnaires, collect documents through email, and reconcile evidence manually. Each handoff adds time without necessarily improving the quality of the final decision.
HITRUST conversations with TPRM leaders reflect the issue. One TPRM leader described their process as tracking vendors in a Google Sheet, distributing questionnaires, and separately collecting security documentation. They only began the assessment once all those materials had been returned.
The problem is larger than the absence of a workflow platform. Digitizing the same questionnaire and document chase can preserve the underlying inefficiency. Programs need consistent assessment methods, reusable evidence, and automation that removes administrative work from trained analysts.
What the Evidence Shows
New 3rd party research coming soon from HITRUST and CHIME* surveyed over 100 qualified TPRM leaders and found that:
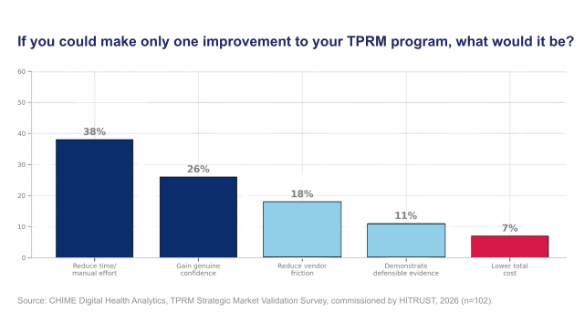
- The most selected improvement in the CHIME survey was “Reduce time and/or manual effort”, chosen by 38.2% of respondents.

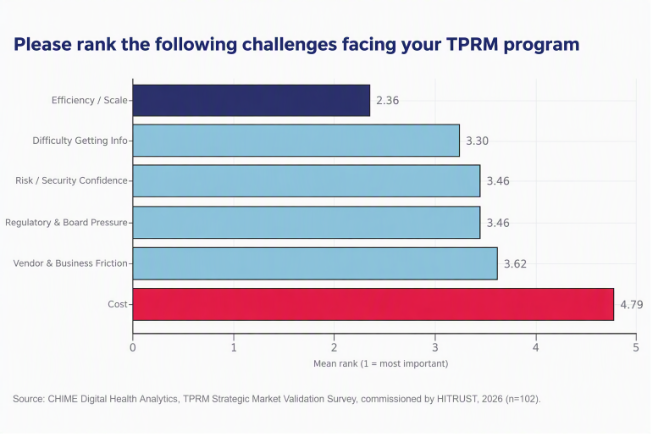
- “Efficiency/Scale” was identified as the highest ranked challenge facing TPRM programs
- According to the Mitratech 2025 Third-Party Risk Management Study, 41% of respondents still used spreadsheets as their primary TPRM tool.
What TPRM Leaders Can Do
- Use tools to centrally manage vendor evidence, records and monitoring so reviewers do not reconstruct the vendor record for each decision.
- Automate routine evidence collection, control mapping, reminders, and reassessment triggers.
- Use AI-assisted review where it can accelerate interpretation, while keeping human judgment focused on scope, exceptions, and material risk.
- Automation should change where people spend their time. The measure of progress is whether analysts have more capacity to evaluate risk and support timely decision
Coming Up in the Next Blog in the Series
If you missed the first blog in the series, please check out it here. Be sure to follow HITRUST on LinkedIn and X to know when the next blog in the TPRM Top 10 series, Hidden Vendor Risks, is posted.
*CHIME Digital Health Analytics. Third-Party Risk Management Assurance: Strategic Market Validation Survey. Commissioned by HITRUST. Ann Arbor, MI: College of Healthcare Information Management Executives, Digital Health Analytics 2026. In July 2026, HITRUST commissioned CHIME Digital Health Analytics to conduct a blinded market-validation survey of 102 qualified respondents from separate healthcare provider organizations with more than $1 billion in annual revenue. Respondents represented security and GRC leadership, TPRM ownership, procurement and vendor management, legal and contracting, and executive leadership. Every participating organization actively managed at least 200 third-party vendors, and 87% managed more than 500.
The TPRM Top 10 - Manual Work Is Consuming TPRM Capacity The TPRM Top 10 - Manual Work Is Consuming TPRM Capacity
Inconsistent scoring and reporting methods make it difficult to compare assurance reports and results across vendors.
Why It Matters
TPRM teams receive multiple forms of evidence to evaluate: Questionnaires, SOC 2 reports, HITRUST certification reports, penetration test results, vulnerability scans, and much more. Each artifact answers different questions and may use a different scope, testing method, treatment of exceptions, and reporting format. Reviewers must normalize the evidence before they can compare vendors or explain why one finding matters more than another.
That work depends heavily on analyst experience and repeated interpretation. Two vendors can appear to provide similar assurance while covering different systems or controls. The same weakness can be described in different terms or reported at a different level of detail. Comparison becomes a manual judgment exercise rather than a repeatable program capability.
What the Evidence Shows
New 3rd party research coming soon from HITRUST and CHIME* surveyed over 100 qualified TPRM leaders and found that:
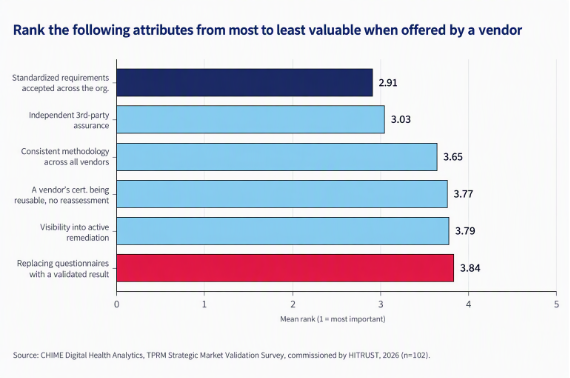
- Standardized requirements accepted across the organization and independent third-party assurance were the two most-valued attributes in the future-state model.

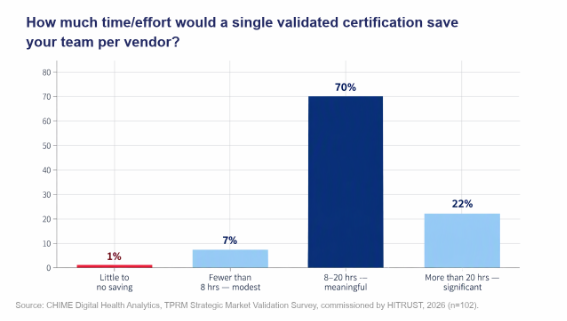
- 92% of respondents estimated that relying on a single validated certification could save at least eight hours per vendor assessment. An organization assessing 100 vendors per year could save 800 hours, or 100 business days, by utilizing this strategy.

What TPRM Leaders Can Do
- Define a consistent baseline for scope, control coverage, testing, and exception reporting across assurance mechanisms.
- Use common criteria to evaluate the relevance and severity of findings, regardless of the format in which they arrive.
- Increase reliance on standardized, independently validated evidence that can be reused across vendor relationships.
- Reserve supplemental requests for material gaps in coverage instead of repeating evidence already validated.
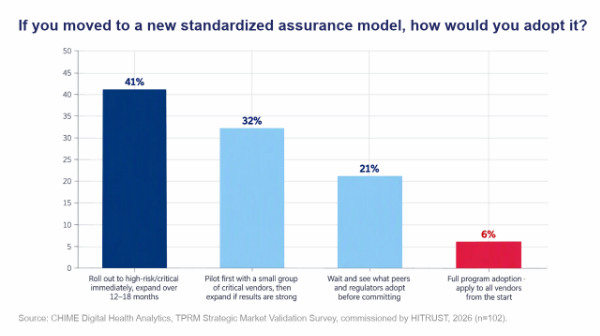
Requiring a single standardized certification can provide tremendous benefit to TPRM programs, both in reducing risk and increasing efficiency. Standardized independent validation can provide a more comparable baseline across a TPRM program’s vendors. When moving to adopt a standardized assurance model, the CHIME survey reported mixed results with how TPRM leaders would approach the process. Most programs (41%) would roll it out to high-risk vendors immediately and then expand to other vendors over the next year, while others (32%) would prefer to pilot first with a smaller group of those critical vendors.
The goal is not to conduct the same exhaustive assessment for every vendor, but to produce enough trustworthy information to identify material exposures early and direct limited expertise toward the risks capable of causing the greatest business impact.
Coming Up in the Next Blog in the Series
If you missed the first blog in the series, please check out it here. Be sure to follow HITRUST on Linkedin and X to know when the next blog in the TPRM Top 10 series, Manual Work Is Consuming TPRM Capacity, is posted.
*CHIME Digital Health Analytics. Third-Party Risk Management Assurance: Strategic Market Validation Survey. Commissioned by HITRUST. Ann Arbor, MI: College of Healthcare Information Management Executives, Digital Health Analytics 2026. In July 2026, HITRUST commissioned CHIME Digital Health Analytics to conduct a blinded market-validation survey of 102 qualified respondents from separate healthcare provider organizations with more than $1 billion in annual revenue. Respondents represented security and GRC leadership, TPRM ownership, procurement and vendor management, legal and contracting, and executive leadership. Every participating organization actively managed at least 200 third-party vendors, and 87% managed more than 500.