If you liked this webinar, you may also be interested in:
Incomplete or unreliable information weakens risk decisions and delays action.
Why it Matters
For vendors already known to the organization, the central challenge is often the quality of the information available. Assurance artifacts may omit critical details, provide vague descriptions, or fail to demonstrate the vendor’s actual security posture. TPRM teams then spend additional time asking questions and requesting evidence that should have been clear at the outset.
“I don’t like wasting time with them back and forth, back and forth, back and forth.” -- TPRM Leader commenting on the challenges with vendor evidence
Poor data can distort onboarding approval decisions, risk tiering, and offboarding resulting in higher risk to the organization. If a relationship is misclassified or its scope is misunderstood, the organization may apply the wrong level of due diligence throughout the vendor lifecycle.
What the Evidence Shows
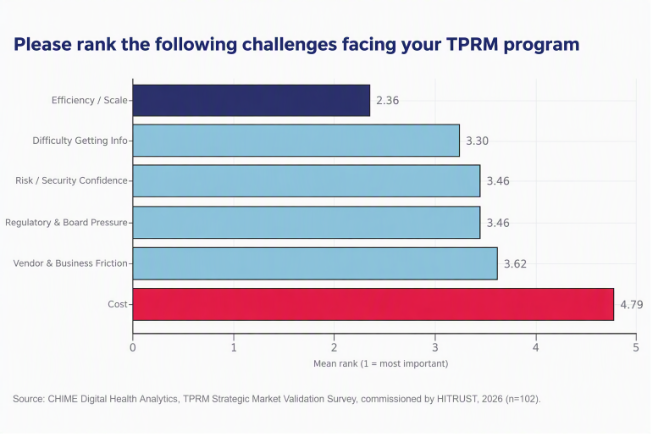
- New 3rd party research coming soon from HITRUST and CHIME* surveyed over 100 qualified TPRM leaders and found that “Difficulty getting information” ranked as the second most important challenge.

TPRM leaders consistently describe to HITRUST their problems receiving assurance artifacts that leave critical questions unanswered regarding scope, inherited controls, fourth-party dependencies, and actual security effectiveness.
What TPRM Leaders Can Do
- Set minimum information requirements for scope, data handling, control coverage, and exceptions.
- Use standardized, independently validated evidence to improve consistency and reduce repeated follow-up.
- Treat data quality as a control over the TPRM process because weak inputs can invalidate sound review methods..
TPRM programs do not need more documents for their own sake. They need complete, trustworthy, and decision-ready information that can support consistent risk judgments.
Coming Up in the Next Blog in the Series
If you missed the first blog in the series, please check out it here. Be sure to follow HITRUST on LinkedIn and X to know when the next blog in the TPRM Top 10 series, Vendor Risk Is Changing Faster Than Reassessment Cycles, is posted.
*CHIME Digital Health Analytics. Third-Party Risk Management Assurance: Strategic Market Validation Survey. Commissioned by HITRUST. Ann Arbor, MI: College of Healthcare Information Management Executives, Digital Health Analytics 2026. In July 2026, HITRUST commissioned CHIME Digital Health Analytics to conduct a blinded market-validation survey of 102 qualified respondents from separate healthcare provider organizations with more than $1 billion in annual revenue. Respondents represented security and GRC leadership, TPRM ownership, procurement and vendor management, legal and contracting, and executive leadership. Every participating organization actively managed at least 200 third-party vendors, and 87% managed more than 500.
The TPRM Top 10 - Unreliable Vendor Data Undermines Risk Decisions The TPRM Top 10 - Unreliable Vendor Data Undermines Risk Decisions
Heavy dependence on a small number of providers can turn one vendor incident into a broader enterprise disruption.
Why It Matters
Traditional vendor reviews examine one relationship at a time. Concentration risk only becomes visible when the organization steps back and looks across the portfolio. Several vendors may rely on the same cloud platform, data processor, software, or geography. A single disruption can therefore affect multiple business processes at once, even when each direct vendor appeared manageable on its own.
The risk is especially pronounced when the underlying provider supports critical operations and few substitutes exist. The same factors that make a vendor strategically important can also make recovery slower, migration more expensive, and business pressure more intense. Relationship-level approval does not answer the portfolio-level question of how much dependency the enterprise has accumulated.
“…a single vulnerability in a third party can quickly ripple across the entire business, grinding operations to a halt.” -- KPMG 2026 Global Third-Party Risk Management Survey
What the Evidence Shows
- According to the2023 EY Global Third-Party Risk Management Survey, only 9% of organizations included concentration risk in the Risk Inventory Reporting process.
- Avoiding concentration risk requires understanding the supply chain. In the Panorays 2025 CISO Survey, only 3% of organizations had full insight across their entire supply chain.
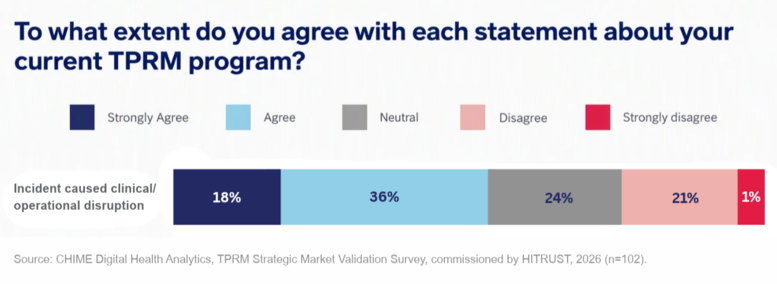
- New 3rd party research coming soon from HITRUST and CHIME* surveyed over 100 qualified TPRM leaders and found that vendor incidents had already caused clinical or operational disruption for approximately 22% of respondents.

What TPRM Leaders Can Do
- Map critical business processes to the vendors and shared service providers that support them into a portfolio for enhanced visibility.
- Analyze concentration by provider, platform, service category, and geography across the portfolio.
- Include downstream providers when evaluating concentration and continuity exposure.
- Define contingency, substitution, and exit plans for dependencies that exceed the organization’s practical tolerance.
Concentration risk is often created gradually, one reasonable vendor decision at a time. Managing it requires a portfolio view that shows where several acceptable relationships combine into one unacceptable dependency
Coming Up in the Next Blog in the Series
If you missed the first blog in the series, please check out it here. Be sure to follow HITRUST on LinkedIn and X to know when the next blog in the TPRM Top 10 series, Unreliable Vendor Data Undermines Risk Decisions, is posted.
*CHIME Digital Health Analytics. Third-Party Risk Management Assurance: Strategic Market Validation Survey. Commissioned by HITRUST. Ann Arbor, MI: College of Healthcare Information Management Executives, Digital Health Analytics 2026. In July 2026, HITRUST commissioned CHIME Digital Health Analytics to conduct a blinded market-validation survey of 102 qualified respondents from separate healthcare provider organizations with more than $1 billion in annual revenue. Respondents represented security and GRC leadership, TPRM ownership, procurement and vendor management, legal and contracting, and executive leadership. Every participating organization actively managed at least 200 third-party vendors, and 87% managed more than 500.
The TPRM Top 10 - Concentration Risk Turns Vendor Failures Into Enterprise Events The TPRM Top 10 - Concentration Risk Turns Vendor Failures Into Enterprise Events
Organizations often lack a clear view of the subcontractors and other downstream parties supporting their most critical vendors.
Why It Matters
Most TPRM programs are designed around direct contractual relationships. The service delivered by a third party, however, may depend on a deeper network of providers that store data, host applications, supply software, or support critical operations. Those fourth and deeper parties (often referred to as 4th or Nth parties) can affect the organization without appearing in its vendor inventory or participating directly in its assurance process.
“We just have so many problems from a fourth-party perspective of getting a good understanding of who all is involved, right? And some of our third parties are like, here have this report. It'll give you all the answers you need and some of it's so vague.” -- TPRM Leader commenting on their challenges with vendor assurance
The blind spot becomes more serious when assurance documentation is vague about subservice organizations, inherited controls, and shared responsibilities. A report may appear comprehensive while excluding the provider that operates an important part of the service. The TPRM team must then determine whether the dependency was assessed, carved out, or left unexamined.
What the Evidence Shows
- According to the 2025 Panorays CISO survey, only 3% of organizations had full insight across their entire supply chain
- In the World Economic Forum Global Cybersecurity Outlook 2026, 78% of CEOs of highly resilient organizations cited supply chain and third-party dependencies as the most significant challenge to further strengthening resilience.
- Require key vendors to disclose the downstream providers supporting material services and data flows.
- Determine whether those providers and their controls are included in the assurance scope, or any supporting evidence.
- Seek separate assurance when a material dependency is excluded.
- Require notification when significant subcontractors, platforms, or service dependencies change.
What TPRM Leaders Can Do
Organizations may outsource a service, but they still retain the risk created by the supply chain behind it. Visibility must extend far enough to understand who supports critical outcomes and where assurance stops.
Coming Up in the Next Blog in the Series
If you missed the first blog in the series, please check out it here. Be sure to follow HITRUST on LinkedIn and X to know when the next blog in the TPRM Top 10 series, Concentration Risk Turns Vendor Failures Into Enterprise Events, is posted.
*CHIME Digital Health Analytics. Third-Party Risk Management Assurance: Strategic Market Validation Survey. Commissioned by HITRUST. Ann Arbor, MI: College of Healthcare Information Management Executives, Digital Health Analytics 2026. In July 2026, HITRUST commissioned CHIME Digital Health Analytics to conduct a blinded market-validation survey of 102 qualified respondents from separate healthcare provider organizations with more than $1 billion in annual revenue. Respondents represented security and GRC leadership, TPRM ownership, procurement and vendor management, legal and contracting, and executive leadership. Every participating organization actively managed at least 200 third-party vendors, and 87% managed more than 500.